
If you run a WordPress website, security should never be something you think about only after a problem appears. Hackers constantly look for outdated software, weak passwords, and other common vulnerabilities that make websites easy targets.
The good news is that improving your WordPress security doesn’t have to be complicated. A few smart changes can significantly reduce the risk of malware, hacking attempts, and data loss.
In this guide, we’ll cover practical ways to make your WordPress website more secure, whether you’re running a personal blog, business website, or online store.
WordPress Security by the Numbers
WordPress powers a large portion of the web, making it one of the biggest targets for automated attacks. The good news is that most successful attacks exploit preventable issues such as outdated plugins, weak passwords, and poor security practices. Keeping your website updated and following basic security tips can dramatically reduce your risk.
Here are a few recent WordPress security statistics:
- WordPress powers more than 43% of all websites on the internet, making it the world’s most widely used content management system.
- More than 11,300 new vulnerabilities were disclosed across the WordPress ecosystem in 2025, highlighting the importance of keeping WordPress, themes, and plugins updated.
- Around 91% of newly disclosed WordPress vulnerabilities were found in plugins rather than WordPress core, making plugin maintenance one of the most important security tasks.
- Wordfence blocked more than 54 billion malicious requests and over 55 billion password attacks against WordPress websites during 2024, showing how frequently websites are targeted by automated attacks.
- Security researchers have found that attackers often begin exploiting newly disclosed WordPress vulnerabilities within hours of a patch being released, making timely updates critical.
1. Keep WordPress Updated
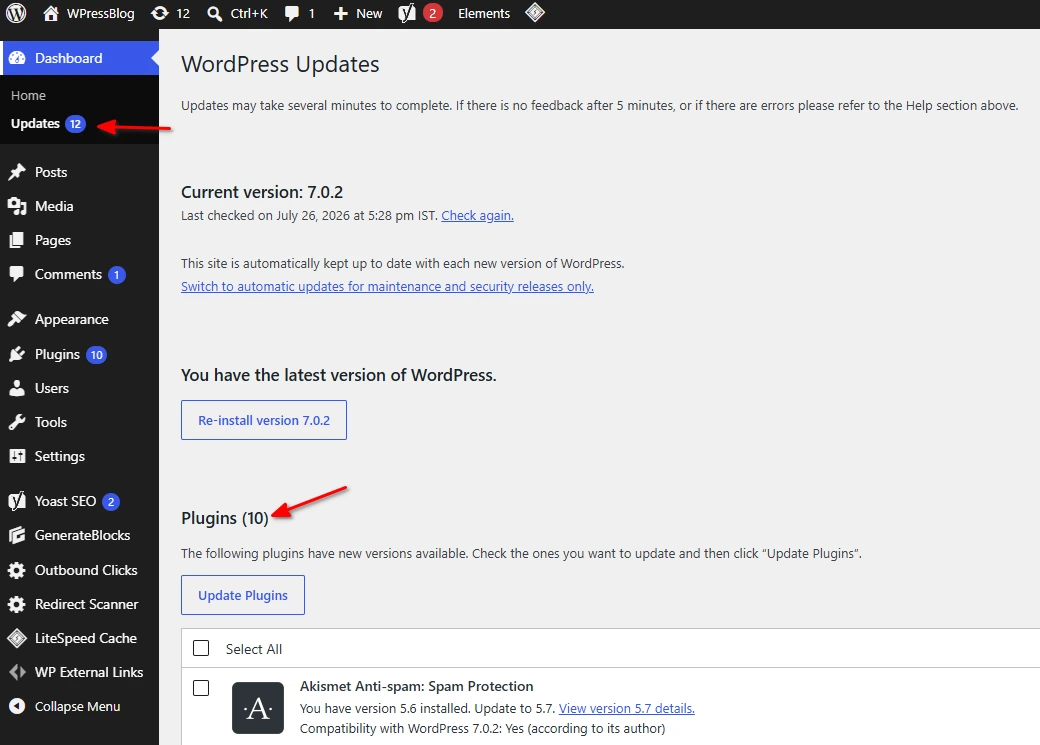
Running an outdated version of WordPress is one of the easiest ways to put your website at risk. Every new WordPress release includes bug fixes, performance improvements, and security patches that protect your site from newly discovered vulnerabilities. The same applies to themes and plugins.
Hackers often scan the internet for websites running outdated software because known vulnerabilities are much easier to exploit than unknown ones.
What You Should Update
Regularly check for updates to:
- WordPress core
- Installed plugins
- Active theme
- Inactive themes
- PHP version (through your hosting provider)
Keeping all of these updated helps close security gaps before attackers can take advantage of them.
Enable Automatic Updates When Possible
If you don’t log into your dashboard frequently, automatic updates can prevent your site from falling behind.
Automatic updates are especially useful for:
- Minor WordPress core releases
- Security patches
- Trusted plugins that receive regular maintenance
For larger updates, it’s still a good idea to create a backup before updating in case of compatibility issues.
Don’t Ignore Plugin Updates
Many website owners update WordPress itself but forget about plugins.
Since plugins add extra functionality, they’re one of the most common entry points for hackers. Even popular plugins occasionally release emergency security patches, so delaying updates can leave your site exposed.
Remove Software That No Longer Receives Updates
Sometimes a plugin or theme is abandoned by its developer.
Warning signs include:
- No updates for a long time
- Compatibility warnings with recent WordPress versions
- Unanswered support requests
- Security vulnerabilities reported publicly
Replacing outdated software is much safer than continuing to use it.
Quick Tips
- Check for updates at least once a week.
- Test major updates on a staging site if possible.
- Always back up your website before significant updates.
- Remove outdated plugins instead of simply deactivating them.
- Update PHP to a supported version for better security and performance.
2. Use a Secure WordPress Hosting Provider
Choosing a reliable web hosting provider is one of the most important decisions for your website’s security. Without it, even the right security steps may not be enough to keep your site safe.
A reliable hosting company invests in server security, malware prevention, firewalls, and continuous monitoring so many threats are stopped before they ever reach your website.
Features to Look For
Not every hosting company offers the same level of protection.
Choose a provider that includes features like:
- Free SSL certificates
- Web Application Firewall (WAF)
- Malware scanning
- DDoS protection
- Automatic backups
- Server-level caching
- Isolated hosting accounts
- 24/7 security monitoring
- Automatic software updates
These features reduce the chances of your website being compromised.
Shared Hosting vs Managed WordPress Hosting
Budget shared hosting works well for many websites, but managed WordPress hosting offers stronger security.
Managed WordPress hosts often provide:
- WordPress-specific firewall rules
- Faster security updates
- Expert WordPress support
- Malware removal assistance
- Daily backups
- Better server isolation
If your website generates revenue or stores customer information, managed hosting is often worth the investment.
Check the Host’s Security Reputation
Before purchasing a hosting plan, look for:
- Transparent security features
- Regular infrastructure updates
- Backup policies
- Uptime guarantees
- Positive customer reviews about security support
A provider with a strong security track record is more likely to respond quickly if something goes wrong.
Avoid Choosing Hosting Based Only on Price
The cheapest hosting plan isn’t always the best value.
Low-cost providers may limit backups, delay security updates, or offer minimal protection against attacks. Paying slightly more for better security can save you from expensive recovery costs later.
Quick Tips
- Choose a hosting provider known for strong security.
- Verify that automatic backups are included.
- Make sure free SSL is available.
- Prefer hosts with proactive malware monitoring.
- Review the provider’s security features before purchasing.
3. Install an SSL Certificate (HTTPS)
An SSL certificate encrypts the data exchanged between your website and its visitors. Instead of sending information as plain text, HTTPS protects sensitive data from being intercepted during transmission.
Modern browsers also expect websites to use HTTPS, making SSL an essential part of website security.
Why HTTPS Matters
Without SSL, attackers may be able to intercept information such as:
- Login credentials
- Contact form submissions
- Customer information
- Payment details
- Personal data
HTTPS helps prevent this type of data theft.
It Also Builds Visitor Trust
Visitors are much more likely to trust a website that displays the secure padlock icon.
A secure connection is especially important for:
- Online stores
- Membership websites
- Business websites
- Login pages
- Websites collecting personal information
How to Enable HTTPS on Your Website
- Log in to your hosting control panel.
- Open the SSL/TLS or Security section.
- Install or activate a free Let’s Encrypt or premium SSL certificate.
- Change your WordPress URL to https:// under Settings → General.
- Redirect all HTTP traffic to HTTPS.
Most Hosting Providers Offer Free SSL
Many hosting companies now include free SSL certificates that can be activated with just a few clicks.
After enabling SSL:
- Force all traffic to HTTPS.
- Update your WordPress Address and Site Address if needed.
- Fix mixed content warnings.
- Verify that every page loads securely.
Keep Your SSL Certificate Active
An expired SSL certificate can cause browser warnings that scare away visitors.
Regularly verify that:
- The certificate hasn’t expired.
- HTTPS is working across your website.
- New pages and images also load securely.
Quick Tips
- Enable HTTPS immediately after launching your website.
- Redirect all HTTP traffic to HTTPS.
- Renew SSL certificates before they expire.
- Fix mixed content issues promptly.
- Regularly test your website for HTTPS errors.
4. Choose a Secure WordPress Theme
Your theme controls much more than your website’s appearance. It also adds code that runs on every page, which means poorly developed themes can introduce security vulnerabilities.
A well-coded WordPress theme reduces security risks while improving compatibility with future WordPress updates.
Download Themes from Trusted Sources
The safest places to get WordPress themes include:
- The official WordPress Theme Directory
- Reputable premium theme developers
- Well-known WordPress marketplaces
Avoid downloading themes from unknown websites offering paid themes for free.
Stay Away from Nulled Themes
Nulled themes are modified premium themes distributed illegally.
They often contain:
- Hidden malware
- Backdoors
- Spam links
- Malicious scripts
- Obfuscated code
Even if a nulled theme appears to work normally, it may silently compromise your website.
Look for Active Development
A good theme should receive regular updates.
Before installing one, check:
- Update frequency
- Compatibility with the latest WordPress version
- User reviews
- Support quality
- Number of active installations
An actively maintained theme is more likely to receive security fixes quickly.
Install Only the Features You Need
Some multipurpose themes include hundreds of features that many websites never use.
Extra functionality increases code complexity and can introduce unnecessary vulnerabilities. Choosing a lightweight theme reduces your attack surface.
Quick Tips
- Download themes only from trusted developers.
- Never use nulled or pirated themes.
- Keep your active theme updated.
- Delete unused themes from your website.
- Choose themes with a strong update history.
5. Install Plugins Only from Trusted Sources
Plugins are one of WordPress’s biggest strengths, but they can also become one of its biggest security risks when installed carelessly.
A single vulnerable or malicious plugin can expose your website to hackers, even if everything else is properly secured.
Download Plugins from Reliable Sources
The safest places to install plugins are:
- The official WordPress Plugin Directory
- Trusted premium plugin developers
- Well-established WordPress companies
Avoid downloading premium plugins from unofficial websites, forums, or file-sharing platforms.
Check the Plugin Before Installing
Spend a few minutes reviewing the plugin.
Things to look for include:
- Regular updates
- High number of active installations
- Positive user reviews
- Recent compatibility with the latest WordPress version
- Responsive developer support
These indicators often reflect a well-maintained plugin.
Install Only What You Actually Need
Every additional plugin increases the amount of code running on your website.
Instead of installing multiple plugins with overlapping features, choose high-quality plugins that solve multiple needs when appropriate.
A handful of reliable plugins can do far more than dozens you’ll never use. See our list of the must-have WordPress plugins in 2026.
Delete Unused Plugins
Deactivating a plugin isn’t enough.
Inactive plugins still exist on your server and may contain vulnerabilities if left outdated. Remove plugins you no longer use to reduce unnecessary security risks.
Avoid Abandoned Plugins
If a plugin hasn’t been updated for a long time, it may no longer receive security patches.
Consider replacing plugins that:
- Haven’t been updated recently
- Show compatibility warnings
- Have unresolved security issues
- Lack active developer support
Quick Tips
- Install plugins only from trusted sources.
- Research plugins before installing them.
- Update plugins as soon as security patches are released.
- Delete plugins you no longer use.
- Audit your installed plugins regularly to remove unnecessary ones.
6. Remove Unused Themes and Plugins
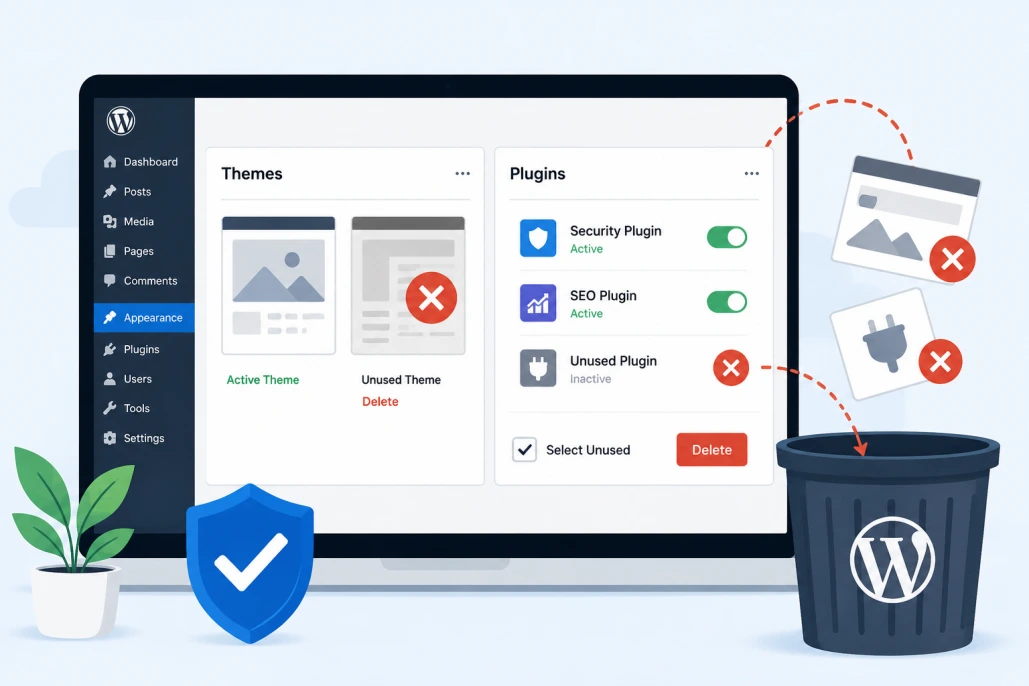
Many website owners deactivate plugins or switch themes but leave the old ones installed. While inactive plugins and themes don’t run on your website, they still exist on your server and can become security risks if they contain vulnerabilities.
Keeping unnecessary software installed increases your website’s attack surface and makes maintenance more difficult.
Why Inactive Software Can Still Be Dangerous
Hackers don’t always target active plugins or themes. If an installed plugin has a known vulnerability, attackers may still be able to exploit it even when it’s inactive.
Unused software can also:
- Contain outdated code
- Include unpatched security vulnerabilities
- Create unnecessary files on your server
- Make website management more complicated
The fewer unnecessary components your website has, the fewer potential entry points hackers have.
Remove Plugins You No Longer Need
It’s common to test several plugins before choosing one.
Once you’ve decided which plugin to use, delete the others instead of leaving them inactive.
Examples include:
- Old SEO plugins after switching to another one
- Backup plugins you no longer use
- Page builders you’ve replaced
- Cache plugins that have been disabled
Keeping only the plugins you actively use makes your website easier to maintain.
Delete Unused Themes
WordPress requires only one active theme.
You may keep one default WordPress theme as a backup for troubleshooting, but every other unused theme should be removed.
For example:
- Active theme
- Latest default WordPress theme (optional)
- Delete every other installed theme
This keeps your installation clean and reduces unnecessary security risks.
Review Your Website Regularly
Every few months, check your installed plugins and themes.
Ask yourself:
- Do I still use this?
- Is it still maintained by the developer?
- Has it received recent updates?
- Is there a better alternative?
If the answer is no, it’s usually best to remove it.
Quick Tips
- Delete inactive plugins instead of simply deactivating them.
- Keep only one backup theme if needed.
- Remove software you no longer use.
- Review installed plugins and themes every few months.
- Replace abandoned plugins with actively maintained alternatives.
7. Use Strong Passwords for Every Account
A weak password can allow hackers to access your website without exploiting any software vulnerability. Password guessing and credential-stuffing attacks are among the most common ways WordPress websites are compromised.
Every account connected to your website should have a unique and strong password.
Which Accounts Need Strong Passwords?
Website security isn’t limited to your WordPress login.
You should secure:
- WordPress administrator accounts
- Editor and author accounts
- Hosting account
- Domain registrar account
- Database login
- FTP/SFTP account
- Email accounts linked to your website
If any one of these accounts is compromised, your website could be at risk.
What Makes a Strong Password?
A secure password should be:
- Long (at least 12–16 characters)
- Random and difficult to guess
- A mix of uppercase and lowercase letters
- Include numbers
- Include special characters
Avoid using:
- Your name
- Website name
- Birthdays
- Phone numbers
- Simple patterns like
123456orpassword
Never Reuse Passwords
Using the same password across multiple websites is risky.
If another website suffers a data breach and your password is exposed, attackers often try the same credentials on WordPress websites.
Using a different password for every account limits the damage if one account is compromised.
Use a Password Manager
Remembering dozens of complex passwords isn’t realistic.
A password manager can:
- Generate strong passwords
- Store them securely
- Fill them automatically
- Help you avoid password reuse
This makes managing strong passwords much simpler.
Quick Tips
- Use unique passwords for every account.
- Make passwords at least 12–16 characters long.
- Never share administrator passwords.
- Change passwords immediately if you suspect a breach.
- Store passwords in a trusted password manager.
8. Enable Two-Factor Authentication (2FA)
Even the strongest password isn’t foolproof. If someone manages to steal or guess it, they can still access your account.
Two-factor authentication (2FA) adds another layer of protection by requiring a second verification step before login.
How Two-Factor Authentication Works
After entering your password, you’ll also need to verify your identity using another method, such as:
- Authentication app code
- One-time verification code
- Security key
- Biometric verification (on supported devices)
Without this second verification step, attackers can’t log in even if they know your password.
Why 2FA Is Worth Enabling
Two-factor authentication helps protect against:
- Stolen passwords
- Brute-force attacks
- Credential stuffing
- Phishing attacks that expose login credentials
It’s one of the most effective ways to secure administrator accounts.
Prioritize Administrator Accounts
If enabling 2FA for every user isn’t practical, start with accounts that have the highest level of access.
These include:
- Administrators
- Shop managers
- Website owners
- Developers
Protecting these accounts significantly reduces security risks.
Use an Authenticator App
Authenticator apps are generally more secure than SMS verification because they aren’t vulnerable to SIM-swapping attacks.
Be sure to store your recovery codes in a safe place so you can regain access if you lose your device.
How to Enable Two-Factor Authentication
- Install a trusted 2FA plugin.
- Enable two-factor authentication for administrator accounts.
- Scan the QR code using an authenticator app.
- Enter the verification code to complete setup.
- Save your recovery codes.
Quick Tips
- Enable 2FA for all administrator accounts.
- Use an authenticator app whenever possible.
- Store recovery codes securely.
- Test your backup login method.
- Encourage team members to use 2FA.
9. Limit Login Attempts
By default, WordPress allows unlimited login attempts. This makes it easier for hackers to run automated brute-force attacks that repeatedly guess usernames and passwords until they find the correct combination.
Limiting login attempts helps stop these attacks before they succeed.
What Is a Brute-Force Attack?
A brute-force attack uses automated software to test thousands or even millions of password combinations.
Attackers often target:
- Administrator accounts
- Common usernames
- Weak passwords
- Websites with no login restrictions
Without login limits, these attacks can continue indefinitely.
How Login Limits Improve Security
When too many failed login attempts occur, your website can temporarily block the user.
Common restrictions include:
- Locking the account after several failed attempts
- Temporarily blocking the IP address
- Increasing the waiting time before another login attempt
- Requiring additional verification
These methods make automated attacks much less effective.
How to Configure Login Attempt Limits
- Install a login security plugin.
- Set the maximum failed login attempts to 3–5.
- Configure a temporary lockout period of 15–30 minutes.
- Enable email notifications for repeated failed logins.
- Review blocked IP addresses regularly.
Monitor Failed Login Attempts
Repeated failed logins may indicate someone is trying to access your website.
Review your login logs for:
- Multiple failed logins
- Unknown IP addresses
- Repeated attempts against administrator accounts
- Login attempts from unusual countries
Early detection allows you to respond before an attack becomes successful.
Don’t Stop Here
To make your login page more secure, also use:
- Strong passwords
- Two-factor authentication
- A firewall
- Login activity monitoring
Using several layers of protection makes your website much harder to compromise.
Quick Tips
- Limit failed login attempts.
- Temporarily block suspicious IP addresses.
- Monitor failed login activity.
- Enable 2FA for administrator accounts.
- Review login logs regularly.
10. Change the Default Admin Username
Many WordPress websites used to create an administrator account named “admin” by default. Although newer WordPress installations require you to choose a username during setup, many older websites still use predictable administrator names.
Since attackers often know or guess common usernames, changing them makes brute-force attacks more difficult.
Why Common Usernames Are Risky
If a hacker already knows your username, they only need to guess your password.
Common administrator usernames include:
- admin
- administrator
- root
- webmaster
- test
Using unique usernames removes one piece of information attackers often rely on.
Choose a Unique Administrator Username
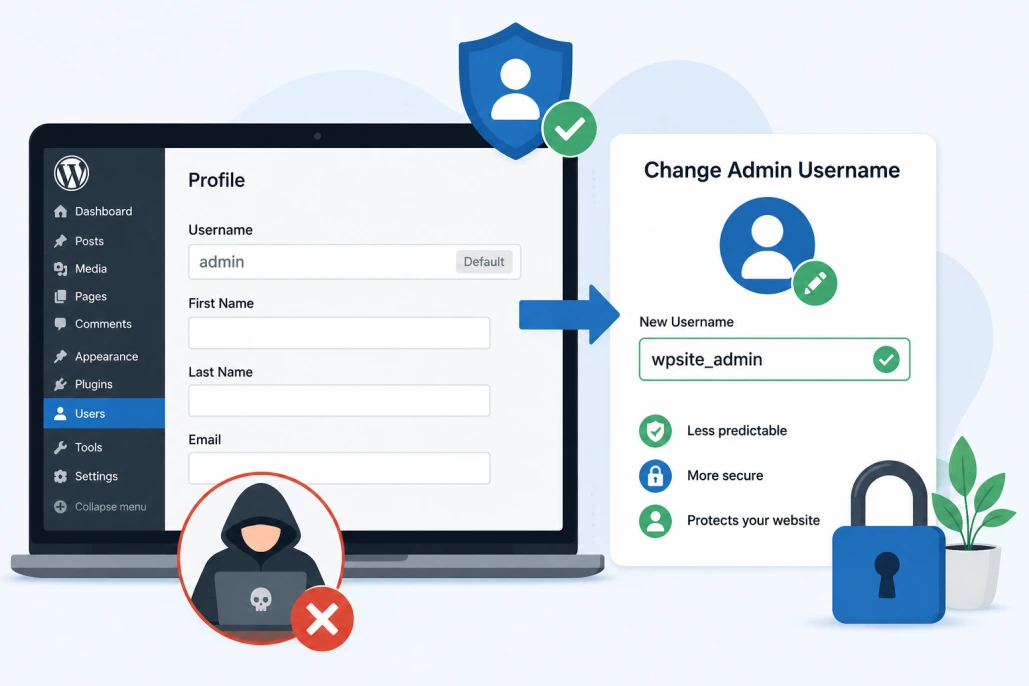
Instead of using obvious names, create something that’s difficult to predict.
Avoid using:
- Your website name
- Your real name
- Generic administrator names
- Email addresses as usernames
A less predictable username increases the effort required to attack your login page.
How to Change the Default Admin Username
WordPress doesn’t allow usernames to be renamed directly.
- Go to Users → Add New.
- Create a new Administrator account with a unique username.
- Log in using the new account.
- Delete the old admin account.
- Assign existing content to the new administrator.
This is the safest way to replace an insecure username.
If you’re not sure how to do this, check out our complete guide on changing the default WordPress admin username with easy, step-by-step instructions.
Hide Your Username Where Possible
Some themes display the administrator username publicly in author archives or profile URLs.
Consider:
- Displaying a nickname instead of the username.
- Reviewing author pages.
- Avoiding usernames that reveal personal information.
Reducing public exposure makes it harder for attackers to identify administrator accounts.
Quick Tips
- Never use “admin” as your administrator username.
- Create a unique administrator account.
- Delete old default administrator accounts.
- Display a nickname instead of your login username.
- Protect your administrator account with a unique username, a strong password, and two-factor authentication.
11. Assign the Right User Roles and Permissions
Not every user needs full control over your WordPress website. One of the simplest ways to improve security is to give users only the permissions they need to perform their tasks.
This approach is known as the Principle of Least Privilege. It limits the damage that can occur if an account is compromised or a user makes a mistake.
Understand WordPress User Roles
WordPress includes several built-in user roles, each with different permissions.
The most common roles are:
- Administrator – Full control over the website.
- Editor – Can manage and publish content from all users.
- Author – Can publish and manage only their own posts.
- Contributor – Can write posts but cannot publish them.
- Subscriber – Can manage only their own profile.
Choosing the correct role helps protect important website settings.
Avoid Giving Administrator Access Unnecessarily
Administrator accounts can:
- Install and delete plugins
- Change themes
- Create or delete users
- Modify website settings
- Access sensitive information
Only trusted people who actually manage the website should have administrator privileges.
Review User Accounts Regularly
Over time, websites often accumulate old user accounts.
Review your user list and remove:
- Former employees
- Old freelancers
- Temporary contributors
- Test accounts
- Inactive users
Removing unused accounts reduces the number of potential entry points.
Update Permissions as Responsibilities Change
A user’s role shouldn’t remain the same forever.
For example:
- Promote contributors only when necessary.
- Downgrade administrator accounts that no longer need full access.
- Remove temporary permissions after a project is completed.
Regular permission reviews help maintain a secure website.
Quick Tips
- Assign the lowest permission level required.
- Limit administrator accounts.
- Delete inactive user accounts.
- Review user roles regularly.
- Update permissions whenever responsibilities change.
12. Keep PHP Updated
WordPress runs on PHP, the programming language that powers most of its core functionality. Running an outdated PHP version can expose your website to security vulnerabilities that are no longer patched.
Keeping PHP updated not only improves security but also enhances website speed and compatibility.
Why PHP Updates Matter
Each supported PHP release includes:
- Security fixes
- Performance improvements
- Bug fixes
- Better memory usage
- Improved compatibility with modern plugins and themes
Older PHP versions stop receiving security updates, making them increasingly risky to use.
Check Your Current PHP Version
Most hosting providers allow you to view your PHP version through the hosting control panel.
You can also check it from:
- WordPress Site Health
- Hosting dashboard
- PHP information tools provided by your host
If your version is no longer officially supported, plan an upgrade as soon as possible.
Test Compatibility Before Updating
Most modern plugins support recent PHP versions, but it’s still wise to test major updates.
Before upgrading:
- Create a complete backup.
- Test on a staging website if available.
- Verify plugin compatibility.
- Check your theme for issues.
This helps avoid unexpected errors after the update.
How to Update Your PHP Version
- Log in to your hosting control panel.
- Open the PHP Version or PHP Selector tool.
- Choose the latest supported PHP version.
- Save the changes.
- Test your website to ensure everything works correctly.
Don’t Delay PHP Upgrades
Many website owners postpone PHP updates because their website appears to be working fine.
However, unsupported PHP versions no longer receive security patches, leaving known vulnerabilities exposed.
Keeping PHP current is an important part of long-term website maintenance.
Quick Tips
- Use a supported PHP version.
- Check for PHP updates regularly.
- Back up your website before upgrading.
- Test compatibility on a staging site.
- Remove outdated plugins that prevent PHP upgrades.
13. Enable Automatic Security Updates
It’s easy to forget about updates, especially if you manage multiple websites. Automatic security updates help ensure that important patches are installed quickly, reducing the time your website remains vulnerable.
The faster a security update is applied, the lower the risk of attackers exploiting a known vulnerability.
What Can Be Updated Automatically?
Depending on your setup, automatic updates can be enabled for:
- WordPress core
- Security releases
- Plugins
- Themes
- PHP (managed by some hosting providers)
Many website owners enable automatic updates for security-related releases while manually reviewing major updates.
Why Automatic Updates Improve Security
Hackers often target websites that haven’t installed recently released security patches.
Automatic updates help by:
- Closing vulnerabilities quickly
- Reducing manual maintenance
- Keeping software current
- Protecting websites when you’re away
This is especially useful for websites that aren’t monitored daily.
Don’t Skip Backups
Although automatic updates are generally reliable, occasional compatibility issues can occur.
Before enabling automatic updates, make sure you also have:
- Regular website backups
- A restore process
- Staging environment (if available)
This allows you to recover quickly if an update causes unexpected problems.
Review Automatic Updates Occasionally
Automation doesn’t eliminate the need for maintenance.
Periodically verify that:
- Updates are installing successfully.
- Plugins remain compatible.
- No update failures are reported.
- Your website functions correctly after updates.
A quick monthly review is usually enough.
Quick Tips
- Enable automatic updates for security releases.
- Review update logs for failed installations.
- Test major updates on a staging site.
- Verify your website after important updates.
- Keep backups before automatic updates.
14. Back Up Your Website Regularly
No security strategy is complete without reliable backups. Even with strong protection in place, unexpected events such as hacking, server failures, accidental deletions, or software conflicts can still happen.
A recent backup allows you to restore your website quickly instead of rebuilding everything from scratch.
What Should a Backup Include?
A complete WordPress backup should contain:
- WordPress files
- Media uploads
- Themes
- Plugins
- Database
- Configuration files
Having only your files or only your database isn’t enough for a full recovery.
Choose a Backup Schedule
The right backup frequency depends on how often your website changes.
For example:
- Daily backups for business websites
- Multiple backups per day for online stores
- Weekly backups for websites with infrequent updates
The goal is to minimize data loss if you need to restore your website.
Store Backups in Multiple Locations
Keeping backups only on the same hosting server is risky.
Instead, store copies in different locations, such as:
- Cloud storage
- External hard drives
- Remote backup servers
- Another secure hosting account
If your server is compromised, you’ll still have a safe copy elsewhere.
For detailed instructions, read our complete guide on how to back up your WordPress website using manual and automatic methods.
You can also save time by using one of the best WordPress backup plugins to schedule backups automatically.
Test Your Backups
A backup is only useful if it can actually be restored.
Periodically test:
- Backup integrity
- Restore process
- Recovery time
- File completeness
Testing ensures you’re prepared before an emergency happens.
Quick Tips
- Create backups automatically.
- Back up both files and the database.
- Store backups offsite.
- Keep multiple backup versions.
- Test the restore process regularly.
15. Use a Reliable WordPress Security Plugin
A security plugin helps monitor, detect, and block threats that could otherwise go unnoticed. While it isn’t a replacement for keeping your website secure, it adds another important layer of protection.
A quality security plugin can continuously watch your website for suspicious activity and alert you before small issues become major problems.
Features to Look For
A good security plugin should offer features such as:
- Malware scanning
- Firewall protection
- Brute-force attack prevention
- Login security
- File integrity monitoring
- Security notifications
- Activity logging
- Vulnerability detection
Different plugins offer different combinations of these features, so choose one that matches your website’s needs.
Avoid Installing Multiple Security Plugins
Running several security plugins at the same time usually doesn’t improve security.
Instead, it can:
- Cause conflicts
- Increase server usage
- Create duplicate scans
- Slow down your website
Choose any of these best security plugins instead of multiple overlapping solutions.
Keep Your Security Plugin Updated
Security plugins receive frequent updates to detect newly discovered threats.
An outdated security plugin may miss:
- New malware signatures
- Recently discovered vulnerabilities
- Improved firewall rules
- Compatibility updates
Treat your security plugin like any other important software and keep it updated.
Review Security Alerts
Security plugins often notify you about:
- Failed login attempts
- Malware detections
- File changes
- Vulnerable plugins
- Suspicious activity
Don’t ignore these notifications. Reviewing alerts regularly allows you to respond before problems become more serious.
Quick Tips
- Install one trusted security plugin.
- Enable malware scanning and firewall protection.
- Keep the plugin updated.
- Review security alerts regularly.
- A security plugin works best as one layer in a broader WordPress security strategy.
16. Protect the wp-admin Area
The wp-admin area is the control center of your WordPress website. Anyone who gains access to it can change settings, install plugins, create users, or even take over your entire site.
Because of this, the admin dashboard is one of the most common targets for hackers. Adding extra layers of protection helps prevent unauthorized access.
Restrict Access to Trusted Users
Only people who manage your website should be able to access the admin area.
Avoid creating unnecessary administrator accounts, and remove access for users who no longer need it.
If you have a team, regularly review who can log in to the dashboard.
Restrict Access by IP Address
If you or your team always log in from the same office or home network, consider limiting access to the wp-admin area by IP address.
This means only approved IP addresses can access the dashboard, while everyone else is blocked before reaching the login page.
Although this isn’t practical for everyone, it’s an excellent option for websites managed from fixed locations.
Log Out Inactive Users Automatically
Leaving an administrator account logged in on a shared or public computer creates unnecessary risk.
Automatic logout features help protect your website by ending inactive sessions after a certain period.
This reduces the chance of someone accessing your dashboard if you forget to log out.
Secure Administrator Devices
Your website is only as secure as the devices used to access it.
Keep administrator computers protected by:
- Installing antivirus software
- Keeping the operating system updated
- Avoiding public Wi-Fi without a VPN
- Locking devices when unattended
Compromised devices can expose even the most secure WordPress website.
Quick Tips
- Limit access to trusted users only.
- Consider IP restrictions for the admin area.
- Automatically log out inactive users.
- Secure devices used for website management.
- Review administrator accounts regularly.
17. Change the Default WordPress Login URL
By default, WordPress login pages are accessible through URLs such as /wp-login.php and /wp-admin. Since these addresses are publicly known, hackers frequently target them with automated login attempts.
Changing the default login URL won’t stop every attack, but it does make your website a less obvious target.
Why Change the Login URL?
Automated bots constantly scan websites looking for the default WordPress login page.
Changing the login URL can help:
- Reduce automated login attempts
- Hide your login page from basic bots
- Lower unnecessary server load
- Reduce brute-force attack activity
Think of it as moving your front door instead of leaving it in the most predictable location.
Don’t Rely on This Alone
Changing the login URL improves security, but it shouldn’t be your only protection.
It works best when you use:
- Strong passwords
- Two-factor authentication
- Login attempt limits
- Security plugins
- Firewall protection
Layered security is always more effective than relying on a single feature.
Choose a Unique Login URL
Avoid replacing the default URL with another obvious choice.
Instead of simple names like:
- /login
- /admin
- /signin
Choose something less predictable that only authorized users know.
Just make sure it’s easy for your team to remember.
If you’re unsure how to change your login URL, check out our guide on how to create and hide a custom WordPress login page.
Save the New Login URL Securely
After changing the login address:
- Bookmark the new login page.
- Store it in a password manager if needed.
- Share it securely with authorized team members.
- Remove outdated bookmarks pointing to the old URL.
Losing the new login URL can make it harder for you to access your own website.
Quick Tips
- Change the default login URL.
- Use a unique, difficult-to-guess address.
- Use 2FA and strong passwords.
- Bookmark the new login page.
- Keep the new login URL private.
18. Disable File Editing from the WordPress Dashboard
WordPress allows administrators to edit theme and plugin files directly from the dashboard. While this feature can be convenient, it also creates a security risk.
If a hacker gains administrator access, they can use the built-in editor to inject malicious code into your website within seconds.
Disabling file editing removes this unnecessary attack vector.
Why Disable the File Editor?
The built-in editor can be abused to:
- Insert malicious PHP code
- Create hidden backdoors
- Modify theme files
- Change plugin functionality
- Maintain long-term access after a hack
Removing dashboard file editing makes these attacks more difficult.
It Doesn’t Affect Normal Website Management
Disabling file editing only removes the editor inside the WordPress dashboard.
You can still:
- Update plugins
- Update themes
- Install new plugins
- Upload themes
- Edit files through SFTP or your hosting File Manager
This makes website management safer without reducing functionality.
Use Secure Methods for File Changes
Whenever you need to edit website files, use secure access methods such as:
- SFTP
- SSH
- Hosting File Manager
- Local development environment
These methods provide better control and are generally more secure than editing files from the dashboard.
How to Disable File Editing
- Open your wp-config.php file.
- Add the following line before the “That’s all, stop editing!” comment:
define( 'DISALLOW_FILE_EDIT', true );- Save the file.
- Refresh the WordPress dashboard.
- Confirm the Theme Editor and Plugin Editor are no longer available.
What Else Helps?
Disabling the file editor is one small but valuable improvement.
It works best alongside:
- Strong administrator passwords
- Two-factor authentication
- File integrity monitoring
- Regular backups
Every extra layer makes unauthorized changes more difficult.
Quick Tips
- Disable the built-in theme and plugin editor.
- Edit files through SFTP or your hosting panel instead.
- Monitor important file changes.
- Limit administrator accounts.
- Test file changes on a staging site whenever possible.
19. Secure the wp-config.php File
The wp-config.php file is one of the most important files in a WordPress installation. It contains your database credentials, authentication keys, and other sensitive configuration settings.
If attackers gain access to this file, they could potentially take complete control of your website.
Why This File Is So Important
The wp-config.php file stores critical information such as:
- Database username
- Database password
- Database host
- Authentication security keys
- WordPress configuration settings
- Debug configuration
Protecting this file is essential because it contains information that should never be publicly accessible.
Restrict File Access
Your server should be configured so that visitors cannot access the wp-config.php file through a web browser.
In addition:
- Apply proper file permissions.
- Prevent direct web access.
- Avoid storing unnecessary sensitive information inside the file.
- Keep server software updated.
These actions significantly reduce the risk of unauthorized access.
How to Secure the wp-config.php File
- Locate the wp-config.php file.
- Change its permissions to 400 or 440 (if supported).
- If your host allows it, move the file one directory above public_html.
- Never share the file publicly.
- Back it up before making changes.
Protect Security Keys
WordPress uses unique authentication keys to encrypt login cookies and sessions.
If these keys are exposed, attackers may be able to hijack user sessions.
If you believe your website has been compromised, regenerating the security keys forces users to log in again and invalidates existing sessions.
Avoid Unnecessary Modifications
Only edit the wp-config.php file when necessary.
Before making changes:
- Create a backup.
- Verify the code you’re adding.
- Avoid copying code from untrusted websites.
- Test your website after modifications.
Small mistakes in this file can cause your website to stop working.
Quick Tips
- Protect the
wp-config.phpfile from public access. - Apply secure file permissions.
- Keep authentication keys secure.
- Back up the file before editing.
- Modify it only when necessary.
20. Protect Important WordPress Files with Proper Permissions
Every file and folder on your server has permissions that determine who can read, modify, or execute it. Incorrect file permissions can allow attackers to change important files or upload malicious code.
Setting proper permissions helps prevent unauthorized access while allowing WordPress to function normally.
Why File Permissions Matter
Permissions control who can:
- Read files
- Modify files
- Execute scripts
- Access directories
If permissions are too open, attackers may be able to alter files or inject malware after exploiting another vulnerability.
Follow Recommended Permission Settings
While exact values may vary depending on your hosting environment, most WordPress websites safely use:
- Files with read and write access only where necessary
- Directories with appropriate execute permissions
- Sensitive configuration files with more restrictive permissions
Avoid granting permissions that allow everyone on the server to modify your website files.
How to Set Correct File Permissions
- Set folder permissions to 755.
- Set file permissions to 644.
- Set wp-config.php to 400 or 440.
- Never use 777 permissions.
- Verify permissions after migrations.
Monitor File Changes
Unexpected file modifications can indicate a security problem.
Regularly monitor:
- Core WordPress files
- Theme files
- Plugin files
- Upload directories
- Configuration files
Many security plugins can alert you when important files change unexpectedly.
Secure Server Access
File permissions are only one part of server security.
Also protect access through:
- SFTP instead of FTP
- Strong hosting passwords
- SSH keys when available
- Limited administrator accounts
Together, these actions make unauthorized file access much more difficult.
Quick Tips
- Use recommended file and directory permissions.
- Avoid overly permissive permission settings.
- Monitor important file changes.
- Use SFTP instead of standard FTP.
- Regularly review server security settings.
21. Disable Directory Browsing
Directory browsing is a server feature that allows visitors to view the contents of folders when no index file is present. If it’s enabled, anyone may be able to see the files and folders inside your WordPress installation.
While directory browsing doesn’t always expose sensitive information directly, it can provide attackers with valuable details about your website’s structure.
Why Directory Browsing Is a Security Risk
If directory browsing is enabled, attackers may discover:
- Plugin directories
- Theme folders
- Uploaded files
- Backup files
- Configuration-related files
- Old installation files
This information can help them identify outdated software or other weaknesses to target.
How Attackers Use Directory Listings
Hackers often examine directory listings to:
- Find vulnerable plugins
- Identify old theme versions
- Search for backup archives
- Locate sensitive files left on the server
The less information you expose publicly, the harder it becomes for attackers to plan an attack.
Verify Whether Directory Browsing Is Enabled
A quick way to check is by opening a folder URL that doesn’t contain an index file.
If you see a list of files instead of an error message or redirected page, directory browsing may be enabled.
Many hosting providers disable it by default, but it’s still worth confirming.
How to Disable Directory Browsing
Directory browsing should be disabled through your web server configuration.
Apache
- Open the .htaccess file.
- Add:
Options -Indexes- Save the file.
Nginx
Add:
autoindex off;Reload Nginx after saving the configuration.
Once disabled:
- Visitors won’t see folder contents.
- Sensitive file listings remain hidden.
- Automated bots receive less information about your website.
This is a simple change that improves overall security.
Quick Tips
- Disable directory browsing on your server.
- Remove unnecessary files from public folders.
- Delete old backup archives from the web directory.
- Periodically verify that folder listings aren’t accessible.
- Keep plugins and themes updated to reduce exposed vulnerabilities.
22. Use a Web Application Firewall (WAF)
A Web Application Firewall (WAF) acts as a protective barrier between your website and incoming traffic. Instead of allowing every request to reach your website, it analyzes requests first and blocks suspicious or malicious ones.
A WAF can stop many attacks before they ever reach WordPress.
What a WAF Can Protect Against
A quality firewall helps defend against:
- Brute-force login attacks
- SQL injection attempts
- Cross-site scripting (XSS)
- Malicious bots
- DDoS attacks
- Known exploit attempts
This reduces the workload on your website while improving security.
Server-Level vs Cloud-Based WAF
There are two common types of firewalls.
Server-level WAF
- Runs on your hosting server.
- Filters traffic before WordPress processes it.
- Often included with managed hosting.
Cloud-based WAF
- Filters traffic before it reaches your hosting server.
- Helps reduce bandwidth usage.
- Can improve website availability during large attacks.
Both provide valuable protection, depending on your hosting environment.
Keep Firewall Rules Updated
Attack techniques change constantly.
A modern firewall regularly updates its:
- Threat database
- Firewall rules
- Bot detection
- IP reputation lists
Using outdated firewall rules reduces its effectiveness against newer attacks.
Take It a Step Further
A firewall should be one layer of your overall security strategy.
For stronger protection, use:
- Strong passwords
- Two-factor authentication
- Security updates
- Malware scanning
- Login protection
Multiple security layers provide much better protection than relying on a firewall alone.
Quick Tips
- Enable a Web Application Firewall.
- Keep firewall rules updated.
- Block malicious bots automatically.
- Use firewall with other security features.
- Review firewall logs periodically.
23. Enable Malware Scanning
Malware can infect a WordPress website without immediately showing obvious signs. Your website may continue working normally while secretly sending spam, redirecting visitors, or giving hackers remote access.
Regular malware scanning helps detect these threats before they cause serious damage.
What Malware Scans Can Detect
Security scans can identify:
- Malicious code injections
- Hidden backdoors
- Suspicious file changes
- Spam scripts
- Known malware signatures
- Unauthorized modifications
Early detection makes cleanup much easier.
Schedule Automatic Scans
Instead of running manual scans occasionally, enable automatic scanning.
Regular scans help identify new threats shortly after they appear.
Many website owners choose:
- Daily scans
- Weekly full scans
- Real-time monitoring (if available)
The right schedule depends on how frequently your website changes.
Review Scan Results Carefully
Not every warning indicates an active infection.
When reviewing scan reports:
- Investigate high-risk alerts first.
- Verify unexpected file changes.
- Update vulnerable plugins immediately.
- Remove infected files only after confirming the issue.
Taking time to review reports helps avoid unnecessary actions.
Don’t Ignore Malware Warnings
If malware is detected:
- Put your website into maintenance mode if necessary.
- Restore a clean backup if available.
- Remove malicious files.
- Update all software.
- Change administrator passwords.
The faster you respond, the less damage malware can cause.
Quick Tips
- Enable automatic malware scanning.
- Review scan reports regularly.
- Investigate suspicious file changes.
- Remove malware immediately after confirmation.
- Keep backups in case a full restoration is required.
24. Monitor Website Activity and Login Logs
Website activity logs record important actions performed on your WordPress site. They provide valuable insight into who logged in, what changes were made, and whether suspicious activity occurred.
Monitoring these logs helps you detect security issues before they become major problems.
What Activity Logs Can Show
Depending on your logging system, you may see:
- User logins
- Failed login attempts
- Plugin installations
- Theme changes
- User account creation
- Content updates
- Settings modifications
These records help you understand exactly what happened on your website.
Watch for Unusual Login Activity
Pay attention to login behavior such as:
- Multiple failed login attempts
- Logins from unfamiliar countries
- Administrator logins at unusual times
- New devices accessing administrator accounts
These events may indicate attempted unauthorized access.
Track Administrative Changes
Unexpected changes deserve immediate attention.
Review logs for:
- Plugin installations you didn’t perform
- Deleted users
- New administrator accounts
- Modified security settings
- Unexpected file changes
The sooner suspicious activity is discovered, the easier it is to investigate.
Keep Activity Logs for Future Reference
Logs can be extremely helpful after a security incident.
They allow you to:
- Identify when an attack started.
- Determine which accounts were involved.
- Understand what was changed.
- Improve future security features.
Maintaining historical logs makes troubleshooting much easier.
Quick Tips
- Enable website activity logging.
- Monitor administrator actions regularly.
- Investigate unusual login attempts.
- Store logs securely.
- Review activity reports on a regular schedule.
25. Protect Against Brute Force Attacks
Brute-force attacks are one of the most common threats facing WordPress websites. Instead of exploiting software vulnerabilities, attackers repeatedly try different username and password combinations until they successfully log in.
Although these attacks are simple, they can be very effective against websites with weak login security.
How Brute Force Attacks Work
Attackers use automated tools that can:
- Try thousands of passwords
- Target multiple usernames
- Run continuously for hours or days
- Launch attacks from multiple IP addresses
Without proper protection, even moderately weak passwords may eventually be guessed.
Use Multiple Layers of Protection
No single security feature completely prevents brute-force attacks.
For the best protection, use:
- Strong passwords
- Two-factor authentication
- Login attempt limits
- Web Application Firewall
- Unique administrator usernames
- Updated WordPress software
Each layer makes automated attacks significantly more difficult.
Monitor for Repeated Login Attempts
Repeated failed logins often indicate that bots are targeting your website.
Watch for:
- Large numbers of failed logins
- Login attempts from unknown countries
- Repeated attacks on administrator accounts
- Sudden spikes in login requests
Early detection allows you to respond before attackers succeed.
Keep Login Security Up to Date
Attack methods continue to evolve, so your defenses should too.
Regularly review:
- Login security settings
- Firewall rules
- User accounts
- Password policies
- Security plugin alerts
A few minutes of routine maintenance can prevent much larger problems later.
Quick Tips
- Block repeated login attempts.
- Use multi-layer login protection.
- Filter malicious login requests before they reach WordPress.
- Monitor authentication activity.
- Review administrator accounts regularly.
26. Secure XML-RPC (Disable It if Not Needed)
XML-RPC is a WordPress feature that allows remote applications and services to communicate with your website. While it can be useful for certain integrations, it’s also a common target for attackers because it can be abused for brute-force attacks and other malicious activities.
If your website doesn’t rely on XML-RPC, disabling it is usually the safest option.
What Is XML-RPC Used For?
Although less common today, XML-RPC can still be used for:
- Remote publishing tools
- Some mobile applications
- Legacy WordPress integrations
- Certain third-party services
Many modern websites no longer require it because the WordPress REST API has replaced most of its functionality.
Why XML-RPC Can Be Risky
Attackers often target XML-RPC to:
- Launch large-scale brute-force attacks
- Abuse the
system.multicallfeature to test many passwords at once - Perform DDoS amplification attacks
- Probe websites for vulnerabilities
Leaving XML-RPC enabled when it’s not needed increases your attack surface.
Check Whether Your Website Uses XML-RPC
Before disabling XML-RPC, verify whether any services depend on it.
For example, consider whether you use:
- Remote publishing software
- Older mobile apps
- Third-party tools that specifically require XML-RPC
If none of these apply, disabling the feature is unlikely to affect your website.
Disable or Restrict Access
If XML-RPC isn’t required:
- Disable it completely.
- Block unnecessary requests.
- Monitor failed XML-RPC requests.
- Keep WordPress updated to reduce related vulnerabilities.
If you must keep it enabled, use a firewall and other security methods to restrict abuse.
How to Disable XML-RPC
Apache
Add to .htaccess:
<Files xmlrpc.php>
Order Deny,Allow
Deny from all
</Files>
Nginx
location = /xmlrpc.php {
    deny all;
}
If an application requires XML-RPC, restrict access instead of disabling it completely.
Quick Tips
- Disable XML-RPC if your website doesn’t use it.
- Verify compatibility before turning it off.
- Monitor XML-RPC activity.
- Protect it with a firewall if it must remain enabled.
- Keep WordPress and plugins updated.
27. Use a Content Delivery Network (CDN) with Security Features
A Content Delivery Network (CDN) is primarily used to improve website speed by serving content from servers located around the world. However, many modern CDNs also include powerful security features that help protect WordPress websites from online threats.
Using a CDN with built-in security adds another layer of defense before traffic even reaches your hosting server.
Security Features Offered by Modern CDNs
Depending on the provider, a CDN may include:
- DDoS protection
- Web Application Firewall (WAF)
- Bot detection
- Rate limiting
- IP reputation filtering
- Automatic HTTPS support
These features help filter malicious traffic while allowing legitimate visitors to access your website.
How a CDN Improves Security
Instead of sending every request directly to your server, a CDN analyzes incoming traffic first.
This helps:
- Block malicious bots
- Reduce automated attacks
- Prevent traffic spikes from overwhelming your server
- Protect against certain types of DDoS attacks
Filtering traffic before it reaches your website improves both security and reliability.
Additional Performance Benefits
Besides security, a CDN can also:
- Reduce page loading times
- Improve global website performance
- Lower server load
- Cache static content
- Improve user experience
The combination of performance and security makes a CDN a valuable investment for many WordPress websites.
Choose a Reputable CDN Provider
When comparing CDN services, look for features such as:
- Built-in firewall protection
- Global server network
- DDoS mitigation
- SSL support
- Security rule customization
- Real-time traffic monitoring
Choosing a provider with strong security capabilities offers better long-term protection.
Quick Tips
- Use a CDN with built-in security features.
- Enable DDoS protection.
- Activate HTTPS through your CDN.
- Monitor CDN security reports.
- Keep firewall rules properly configured.
28. Scan Your Website for Vulnerabilities Regularly
Malware scans help detect infections, but vulnerability scans serve a different purpose. They identify weaknesses in your website before hackers can exploit them.
Regular vulnerability scanning allows you to fix security issues proactively instead of reacting after an attack.
What Vulnerability Scans Check
A vulnerability scanner may detect:
- Outdated WordPress versions
- Vulnerable plugins
- Insecure themes
- Unsupported PHP versions
- Known security flaws
- Misconfigured settings
These reports help you prioritize security improvements.
Scan After Major Changes
It’s a good idea to perform vulnerability scans after:
- Installing new plugins
- Changing themes
- Updating WordPress
- Migrating your website
- Modifying server settings
This helps ensure new changes haven’t introduced unexpected security risks.
Review Results Promptly
Finding a vulnerability doesn’t necessarily mean your website has been hacked.
Instead:
- Review the reported issue.
- Confirm whether it affects your website.
- Apply available updates.
- Replace vulnerable software if needed.
Responding quickly reduces the opportunity for attackers.
Make Scanning Part of Routine Maintenance
Don’t wait until something goes wrong.
Create a regular schedule for:
- Weekly vulnerability scans
- Monthly security reviews
- Plugin audits
- Software updates
Routine maintenance greatly improves long-term security.
Quick Tips
- Scan your website regularly for vulnerabilities.
- Perform scans after major website changes.
- Update vulnerable software immediately.
- Remove unsupported plugins and themes.
- Schedule routine security maintenance.
29. Monitor Website Uptime and Security Alerts
Security isn’t only about preventing attacks. You also need to know when something goes wrong.
Uptime monitoring and security alerts notify you about potential problems so you can respond quickly before they affect your visitors or business.
Why Uptime Monitoring Matters
Unexpected downtime can be caused by:
- Server failures
- Malware infections
- DDoS attacks
- Plugin conflicts
- Configuration errors
- Expired hosting services
Receiving an alert immediately allows you to investigate before customers notice the issue.
Enable Security Notifications
Many security tools can alert you when they detect:
- Failed login spikes
- Malware infections
- File modifications
- Plugin vulnerabilities
- Firewall blocks
- New administrator accounts
These alerts help you react to suspicious activity much sooner.
Choose the Right Notification Method
Security notifications are most useful when you receive them promptly.
Common notification methods include:
- Email alerts
- Mobile notifications
- Dashboard notifications
- Messaging integrations
Use channels you’ll actually monitor regularly.
Don’t Ignore Repeated Alerts
Receiving the same alert repeatedly may indicate an ongoing issue.
Investigate recurring notifications related to:
- Login attacks
- Malware detections
- Server errors
- Website downtime
- Resource usage spikes
Addressing recurring problems helps prevent larger incidents later.
Quick Tips
- Enable uptime monitoring.
- Turn on important security alerts.
- Investigate repeated notifications promptly.
- Review alert settings regularly.
- Test notification delivery periodically.
30. Perform Regular Security Audits
Website security isn’t something you set up once and forget. As your website grows, you install new plugins, add users, update software, and make configuration changes that can introduce new security risks.
A regular security audit helps ensure your website remains protected over time.
What Should a Security Audit Include?
A comprehensive audit should review:
- WordPress version
- Plugin updates
- Theme updates
- User accounts
- File permissions
- Backup status
- Firewall configuration
- SSL certificate
- PHP version
- Security plugin settings
Reviewing these areas helps identify issues before they become serious.
Remove Unnecessary Access
During each audit, check for:
- Inactive administrator accounts
- Former employees
- Old developer accounts
- Temporary users
- Unused API credentials
Removing outdated access reduces potential entry points for attackers.
Review Installed Software
Take time to inspect:
- Unused plugins
- Abandoned themes
- Unsupported software
- Duplicate functionality
- Plugins with known vulnerabilities
Cleaning up unnecessary software improves both security and website performance.
Create a Recurring Security Checklist
Instead of relying on memory, maintain a checklist that you complete regularly.
Your checklist might include:
- Verify backups
- Install updates
- Review login logs
- Scan for malware
- Run vulnerability scans
- Check SSL status
- Test website restoration
- Review user accounts
A documented process helps ensure important tasks aren’t overlooked.
Quick Tips
- Perform security audits regularly.
- Review users, plugins, and themes.
- Remove unnecessary access.
- Verify backups and recovery procedures.
- Keep a recurring security maintenance checklist.
Common WordPress Security Mistakes to Avoid
Even websites with good security features can become vulnerable because of simple mistakes. In many cases, hackers don’t need advanced techniques—they simply take advantage of poor security habits that could have been avoided.
Below are some of the most common WordPress security mistakes and how to avoid them.
Ignoring WordPress Updates
One of the biggest mistakes is delaying updates for WordPress core, plugins, themes, or PHP.
Outdated software often contains publicly known vulnerabilities that hackers actively scan for.
Instead:
- Install security updates promptly.
- Enable automatic security updates where appropriate.
- Test major updates before deploying them.
Using Weak or Reused Passwords
Weak passwords remain one of the leading causes of hacked WordPress websites.
Avoid passwords that include:
- Your name
- Website name
- Birthdays
- Simple number sequences
- Common words
Also, never reuse the same password across multiple accounts.
Giving Too Many Users Administrator Access
Not every team member needs full control of your website.
Granting unnecessary administrator privileges increases the risk of:
- Accidental changes
- Insider mistakes
- Unauthorized access if an account is compromised
Assign the lowest permission level required for each user.
Installing Plugins or Themes from Untrusted Sources
Free downloads from unofficial websites may seem tempting, but they often contain hidden malware or backdoors.
Only install plugins and themes from:
- The official WordPress repository
- Trusted premium developers
- Reputable WordPress companies
Avoid nulled or pirated software entirely.
Forgetting to Create Backups
Many website owners only think about backups after their website has already been hacked or damaged.
Without recent backups, recovering your website can be extremely difficult.
A good backup strategy should include:
- Automatic backups
- Offsite storage
- Multiple backup versions
- Regular restore testing
Leaving Unused Plugins and Themes Installed
Inactive plugins and themes don’t disappear just because they’re deactivated.
Old software can still contain vulnerabilities that attackers may exploit.
Regularly:
- Delete unused plugins.
- Remove unnecessary themes.
- Replace abandoned software.
Using Default Login Settings
Keeping the default login URL and using predictable administrator usernames makes automated attacks much easier.
Improve login security by:
- Changing the default login URL.
- Avoiding usernames like “admin.”
- Enabling two-factor authentication.
- Limiting login attempts.
Disabling Security Features for Convenience
Some users disable firewalls, malware scanning, or security plugins because they believe they slow down the website.
While performance matters, removing essential security features creates unnecessary risk.
Instead, optimize your website while keeping important security protections enabled.
Ignoring Security Warnings
Security plugins, hosting providers, and monitoring tools often send alerts about potential problems.
Ignoring these notifications can allow small issues to become serious security incidents.
Review alerts related to:
- Malware detection
- Failed login attempts
- Plugin vulnerabilities
- File changes
- Website downtime
Assuming Your Website Is Too Small to Be Targeted
Many people believe hackers only attack large websites.
In reality, automated bots scan millions of websites regardless of their size. Personal blogs, small business websites, and online stores are all common targets because automated attacks don’t discriminate.
Every WordPress website should follow basic security steps, regardless of its traffic or popularity.
WordPress Security Checklist
Use this checklist to quickly review your WordPress website’s security. If you can check off every item below, your website is in a much better position to resist common attacks.
Core Website Security
- Keep WordPress updated to the latest version.
- Update all plugins and themes regularly.
- Use a supported PHP version.
- Enable automatic security updates where appropriate.
- Remove unused plugins and themes.
- Delete abandoned or unsupported software.
Login & User Security
- Use strong, unique passwords for every account.
- Enable two-factor authentication (2FA).
- Change the default administrator username if needed.
- Limit login attempts.
- Change the default WordPress login URL.
- Assign the correct user role to each account.
- Remove inactive user accounts.
- Review administrator accounts regularly.
Server & File Security
- Protect the
wp-adminarea. - Disable the built-in theme and plugin file editor.
- Secure the
wp-config.phpfile. - Apply proper file and folder permissions.
- Disable directory browsing.
- Disable XML-RPC if your website doesn’t require it.
- Use SFTP instead of standard FTP.
Website Protection
- Install a trusted WordPress security plugin.
- Enable a Web Application Firewall (WAF).
- Turn on malware scanning.
- Scan your website regularly for vulnerabilities.
- Monitor website activity logs.
- Review login logs for suspicious activity.
- Enable uptime monitoring and security alerts.
Backup & Recovery
- Schedule automatic website backups.
- Back up both website files and the database.
- Store backups in an offsite location.
- Keep multiple backup versions.
- Test your backups by performing a restoration.
Network & Performance Security
- Install an SSL certificate and force HTTPS.
- Use a CDN with built-in security features.
- Enable DDoS protection if available.
- Keep firewall rules up to date.
- Monitor unusual traffic patterns.
Routine Maintenance
- Review security plugin reports.
- Check for vulnerable plugins and themes.
- Audit user accounts and permissions.
- Verify SSL certificate status.
- Review hosting security settings.
- Perform regular security audits.
- Stay informed about new WordPress security vulnerabilities.
FAQs
Is WordPress secure enough for business websites?
Yes. WordPress is secure enough for business websites when it’s properly maintained. Keeping WordPress, plugins, themes, and PHP updated, using strong passwords, enabling two-factor authentication, and following the other security tips in this guide can significantly reduce the risk of attacks.
What is the biggest security risk for a WordPress website?
The biggest security risks are outdated plugins and themes, weak passwords, poor user access management, and installing software from untrusted sources. These issues are responsible for many successful WordPress attacks.
Do I really need a WordPress security plugin?
While WordPress itself includes basic security features, a dedicated security plugin provides additional protection such as malware scanning, firewall rules, login security, file monitoring, and security alerts. It’s recommended for most websites.
How often should I update my WordPress website?
You should install security updates as soon as they’re available. It’s also a good idea to check for WordPress core, plugin, theme, and PHP updates at least once a week if automatic updates aren’t enabled.
How often should I back up my WordPress website?
The ideal backup frequency depends on how often your website changes. Websites updated daily should have daily backups, while online stores or membership sites may benefit from multiple backups throughout the day.
Is changing the WordPress login URL necessary?
Changing the default login URL isn’t required, but it can reduce automated login attempts and make your website less attractive to basic bots. It should be used alongside stronger security features like 2FA and login attempt limits.
Should I disable XML-RPC in WordPress?
If your website doesn’t use XML-RPC for remote publishing or other required services, disabling it is generally recommended because it reduces potential attack vectors.
Can an SSL certificate protect my website from hackers?
An SSL certificate encrypts data exchanged between your website and visitors, protecting sensitive information during transmission. However, SSL alone doesn’t stop hacking attempts, so it should be used with other security features.
Does a CDN improve WordPress security?
Yes. Many modern CDNs include security features such as DDoS protection, bot filtering, firewall integration, and HTTPS support. These features help block malicious traffic before it reaches your website.
How can I tell if my WordPress website has been hacked?
Common signs include unexpected redirects, unusual administrator accounts, malware warnings, unknown file changes, spam content, suspicious login activity, poor website performance, or visitors reporting security warnings. Regular malware scans and activity monitoring can help detect these issues early.
Can too many plugins make WordPress less secure?
Yes. Every plugin adds more code to your website, which increases the potential attack surface. Instead of installing many plugins, use only well-maintained plugins from trusted developers and remove any you no longer need.
What should I do first if my WordPress website gets hacked?
Immediately put your website into maintenance mode if necessary, change all passwords, restore a clean backup if available, scan for malware, update WordPress and all installed software, remove malicious files, and investigate how the attackers gained access to prevent future incidents.
Final Thoughts
WordPress security is an ongoing process rather than a one-time setup. Regular maintenance, timely updates, user access reviews, and proactive monitoring help reduce risks and keep your website protected as new threats emerge.
The good news is that you don’t need to do everything at once. Start with the basics, then gradually work through the steps in this guide. Spending a little time on security today can save you from costly downtime, data loss, and recovery efforts in the future.
Most importantly, make security part of your regular website maintenance. A few minutes spent reviewing updates, backups, and security alerts each week can go a long way toward keeping your WordPress website safe.
I read this article carefully and applied all the suggested settings. Thank you very much!
Thanks for the great article. It helped me to secure my wordpress website.
Thanks for the nice important content.